
Cybersecurity protects networks, devices and data from unauthorised access or criminal use. It aims to keep information confidential, accurate and available when it is needed, a goal security teams call the CIA triad. That is the working definition used by the US Cybersecurity and Infrastructure Security Agency (CISA). Common threats include phishing, ransomware, malware, insider threats and man-in-the-middle attacks. This article expands on each of these, and also covers the main types of cybersecurity work.
Why cybersecurity matters more each year
The cost of getting this wrong keeps rising. The IBM 2026 Cost of a Data Breach Report puts the global average cost of a breach at $4.99 million. That is a 12% increase over the previous year and a record high, per the official IBM report. In the United States the average cost reaches $11.5 million, according to coverage of the same IBM report. Those figures cover investigation, lost business, downtime and reputational recovery.
Demand for defence grows at a similar pace. MarketsandMarkets projects the global cybersecurity market to grow from $227.59 billion in 2025 to $351.92 billion by 2030. That is a 9.1% annual growth rate, per its market forecast. On the crime side, the FBI Internet Crime Complaint Center recorded 1,008,597 complaints in 2025. Reported losses reached $20.877 billion, a 26% rise over 2024, per the 2025 IC3 Annual Report.
The CIA triad: how security professionals frame the problem
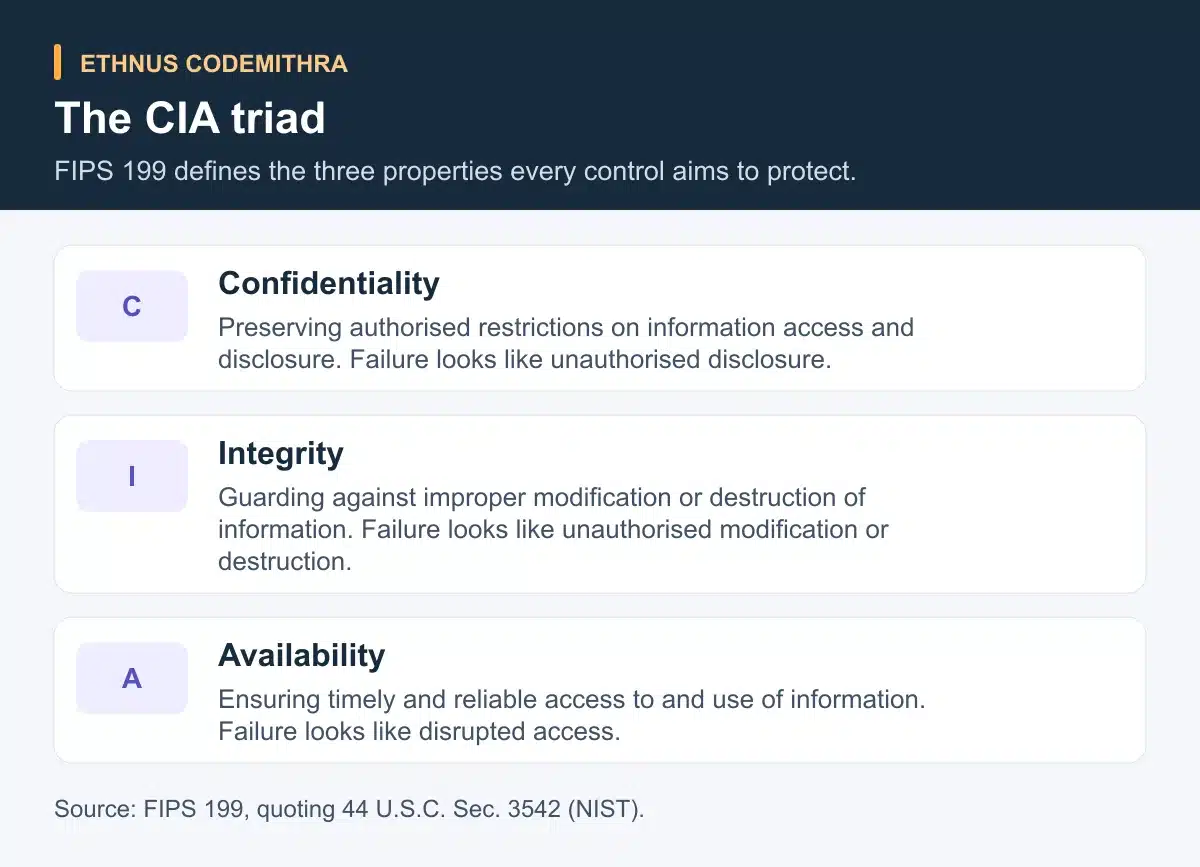
Security teams do not defend against everything equally. They organise the work around three properties, known together as the CIA triad. These are formally defined in the US FIPS 199 standard. Confidentiality means keeping authorised restrictions on who can access or see information. Integrity means guarding against improper change or destruction of information, including proof of where it came from. Availability means making sure the right people can reach information reliably when they need it.
Each pillar has a matching failure mode, and FIPS 199 defines those too. A loss of confidentiality shows up as unauthorised disclosure. A loss of integrity shows up as unauthorised modification or destruction. A loss of availability shows up as disrupted access. Every control an organisation puts in place maps back to one of these three properties. A password policy and a backup schedule are two everyday examples.
Five cyber threats you are likely to meet
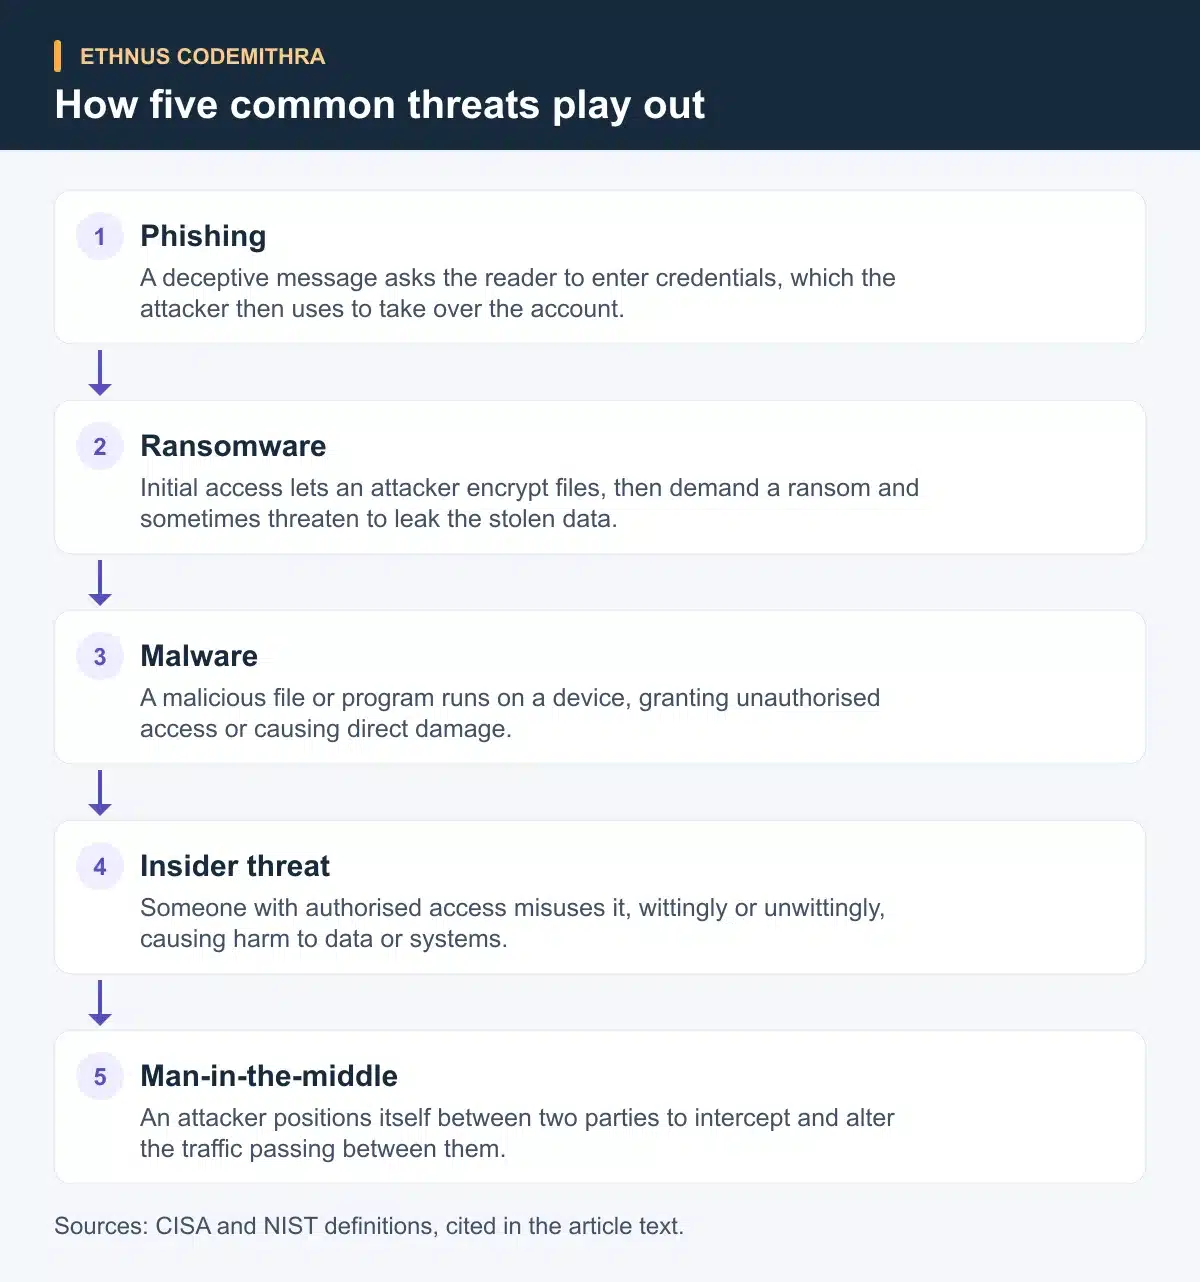
Most incidents trace back to a small set of well-understood threats. Here is how each one actually works, not just its name.
- Phishing. A form of social engineering that uses email or a fake website to pose as a trustworthy organisation, per CISA. The goal is to collect personal information. The victim enters credentials on the fake page, and the attacker uses them to take over the account.
- Ransomware. An evolving form of malware that encrypts files on a device, making them unusable, per the CISA Ransomware 101 guide. Attackers demand a ransom for decryption. Many now also threaten to leak the stolen data if the ransom goes unpaid.
- Malware. CISA's term for unwanted files or programs that can damage a computer or expose the data on it. The category includes viruses, worms and Trojan horses, per CISA. Running the file is usually enough to grant the attacker access or cause damage.
- Insider threat. The risk that someone with authorised access uses it to cause harm, knowingly or unknowingly, per CISA. An insider is anyone who currently has, or previously had, that access. The threat does not need malicious intent to cause real damage.
- Man-in-the-middle attack. An attack where the adversary positions itself between a user and a system, per the NIST glossary. From there it can intercept and alter the data travelling between them. Neither side may notice a third party reading or changing the traffic.
These threats are not equally common. In 2025, phishing and spoofing was the largest crime type IC3 tracked by complaint count, at 191,561 complaints. Ransomware complaints numbered only 3,611. Even so, they caused $32,320,105 in reported losses, per the 2025 IC3 Annual Report. Investment fraud was the costliest category overall, at $8.65 billion.
Types of cybersecurity: what each domain protects
Cybersecurity covers several distinct areas of work. Each protects a different part of an organisation. The IBM cybersecurity overview groups this work into domains such as the six below. Treat this as one widely used way to divide the field, not a single official standard. Neither CISA nor NIST publishes one universal numbered list.
| Domain | What it protects | Typical control example | Source |
|---|---|---|---|
| Network security | Servers, connections and devices that make up a network | Firewalls and network segmentation | CISA |
| Application security | Software, from design through to everyday use | Secure code review and application testing | IBM |
| Cloud security | Data and infrastructure hosted with a cloud provider | Identity-based access policies and encryption | IBM |
| Endpoint security | Laptops, phones and other devices that connect to a network | Endpoint detection and response software | IBM |
| Identity security | Accounts and credentials used to reach systems and data | Multi-factor authentication | IBM |
| Critical infrastructure security | Physical and digital systems that power and water utilities depend on | Strict access control on operational technology | CISA |
Network security itself already spans servers, cloud systems and connected devices, per CISA's guidance on securing networks. That overlap is normal, not a contradiction. One incident can touch several domains at once. A phishing email that leads to ransomware on a cloud server is a common example.
A five-minute self-check using the CIA triad
Before you read further, run this exercise on one account or device you use daily. Your email or your laptop both work well for this.
- Confidentiality. Who else could see your password if it leaked today. Do you reuse that password anywhere else.
- Integrity. If a file changed without your knowledge, would you notice. Do you have a way to check that a download has not changed.
- Availability. If this device failed right now, could you recover your data within an hour. When did you last test a backup, not just create one.
A weak answer to any question points to a real gap, not a hypothetical one. This is the same reasoning a security team applies at organisation scale. It simply starts from one account instead of thousands.
Who works in cybersecurity, and how the Codemithra CSA course teaches it
One common entry-level and intermediate role is the Security Operations Center (SOC) analyst. This person monitors an organisation's systems, investigates alerts and responds to incidents. Codemithra runs a live Certified Security Operations Center Analyst (CSA) course built for this role. It targets current and aspiring Tier I and Tier II SOC analysts.
The course runs 150 hours across six sections and 39 lessons. It prepares students for the EC-Council Certified SOC Analyst exam. The six syllabus modules cover security operations and management, cyber threats and attack methodology, and incidents, events and logging. The remaining three cover SIEM incident detection, threat intelligence, and incident response. The course includes trainer-led sessions, industry-relevant projects, quizzes and assignments, and placement assistance. It currently lists 635 students enrolled with a 4.6 out of 5 rating on the Codemithra courses page.
This article covers the fundamentals under that syllabus, such as the CIA triad and the five threats above. It does not cover exam preparation itself. Ethnus, the group behind Codemithra, reached the milestone of training over 5 lakh students across all its courses. It names cybersecurity among its focus areas, alongside cloud computing, IoT, AI and machine learning, per the Ethnus about page.
Frequently asked questions
What is cybersecurity?
Cybersecurity is the practice of protecting networks, devices and data from unauthorised access or criminal use. It keeps information confidential, accurate and available, per the CISA definition.
What are the main types of cyber threats?
This article covers five threats. They are phishing, ransomware, malware, insider threats and man-in-the-middle attacks. Each has its own mechanism, described above with a CISA or NIST source.
What are the types of cybersecurity, and is there one official list?
No single CISA or NIST document publishes one numbered list. A current industry grouping from IBM covers network, application, cloud, endpoint, identity and critical infrastructure security. See the table above for what each one protects.
What does a SOC analyst do?
A SOC analyst monitors an organisation's systems, investigates security alerts and helps respond to incidents. The Codemithra CSA course trains for this role across six modules. These cover operations, threat methodology, logging, SIEM detection, threat intelligence and incident response.
To move from these fundamentals toward SOC analyst skills, start with the Certified Security Operations Center Analyst (CSA) course on Codemithra.